Implementing zero trust security is often dismissed as an expensive enterprise luxury, yet for modern freelancers handling high-value client access tokens, it represents the single most practical defense against catastrophic cross-account contamination.
Find out what web trackers uncover about your canvas rendering, WebGL parameters, screen dimensions, and hardware fingerprint across every freelance portal you browse.
Select your current operational situation to evaluate your zero trust exposure:
Zero Trust Verdict: High Contamination Risk. Never reuse passwords or browser sessions across clients. Segment each client into an isolated browser profile with dedicated master credentials and zero-knowledge vault entries.
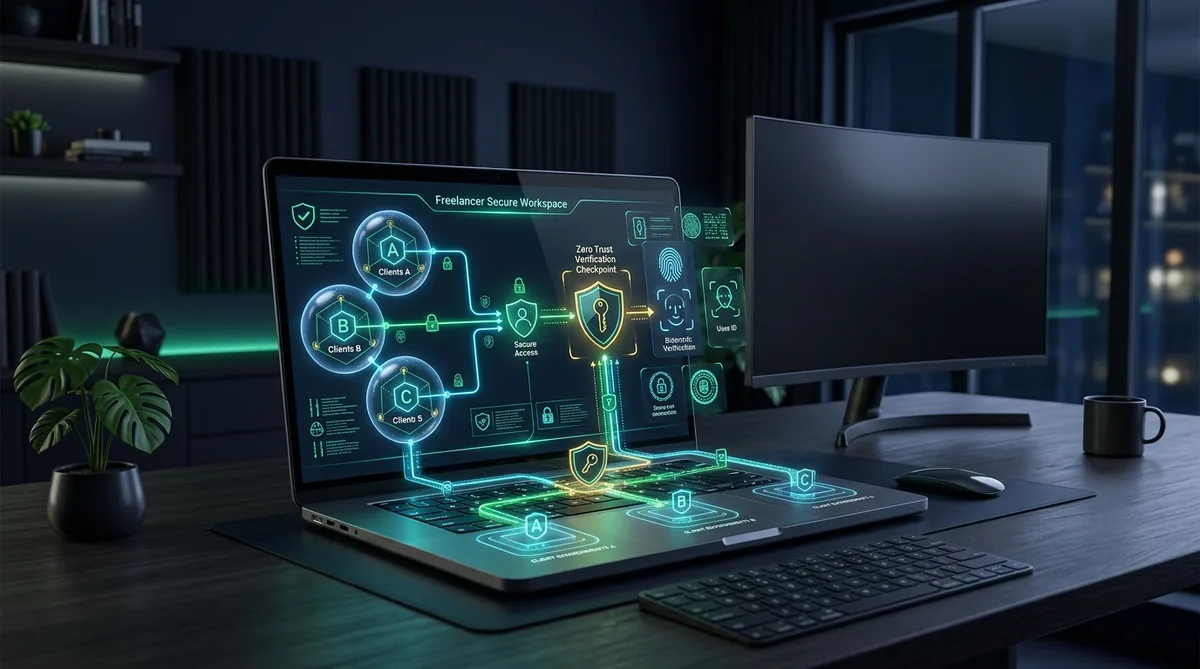
| Core Definition | Zero trust security framework requiring continuous verification for every user, device, and request |
| Primary Freelance Threat | Cross-account contamination where a breach at one client compromises another client’s infrastructure |
| Foundational Tooling | Password managers (Bitwarden/1Password), containerized browser profiles & FIDO2 hardware keys |
| Network Assumption | Assume all local networks (home routers, public Wi-Fi) are actively compromised; encrypt all traffic |
| Implementation Cost | $0 to $10/month (achievable using free tier vaults, built-in browser profiles, and standard MFA apps) |
01 A Genuine Practitioner Debate: Security vs. Daily Friction
A candid discussion in the r/cybersecurity community captures honest, practical skepticism worth hearing: experienced engineers frequently note that zero trust security sounds immaculate in theoretical whitepapers, but in fast-paced production environments, excessive verification prompts can degrade operational velocity and tempt workers to bypass protocols.
For an independent freelancer billing by the hour or juggling tight deadlines, this friction concern is doubly valid. You cannot spend twenty minutes re-authenticating across twelve cloud tabs just to update a client’s staging database. However, this debate overlooks a fundamental shift: modern zero trust security is no longer an all-or-nothing corporate surveillance apparatus. When adapted for solo operators, it is simply a mindset that systematically eliminates blind trust without introducing crippling administrative drag.
02 What Zero Trust Actually Means: Never Trust, Always Verify
To implement defenses effectively, we must demystify corporate buzzwords. Major cybersecurity authorities define the framework with crystal clarity:
As CrowdStrike defines it, Zero Trust is a security framework that mandates strict identity verification for every user and device trying to access resources, regardless of whether they’re inside or outside the organization’s network.
Global cloud and network providers expand upon this foundational rule. Cloudflare’s security glossary frames zero trust around maintaining continuous access controls rather than granting broad perimeter clearance. Similarly, Fortinet emphasizes that no user, device, or application should be inherently trusted based solely on physical location or IP address.
Furthermore, threat intelligence analyses from Huntress highlight that zero trust eliminates implicit trust in any single node, service, or login session. In traditional computing, once you enter a password, the system assumes you are trustworthy indefinitely. In contrast, zero trust security treats every single request as a distinct verification boundary.
03 The Business Case: Financial & Legal Stakes for Solopreneurs
Why should a one-person business care about enterprise architectural models? The financial and reputational justification is overwhelming:
Forrester, the firm that coined the term “Zero Trust,” has long argued that the model’s real payoff is fewer breaches and a smaller blast radius when one does happen — an attacker who compromises one segment doesn’t automatically get the rest of the network.
As a freelancer, you represent an enticing “supply chain backdoor” for attackers. Enterprise clients spend millions hardening their internal networks, but they regularly grant administrative credentials to outside contractors. If your unsegmented laptop is compromised, cybercriminals can ride your saved sessions straight into the client’s core repositories.
Modern service agreements increasingly feature stringent cybersecurity indemnification clauses. If negligence on your local workstation precipitates a client data breach, you face immediate contract termination, severe reputational ruin, and potential civil litigation. Enforcing zero trust security protects your personal livelihood just as much as it shields your clients.
04 Implementing Zero Trust Security: The 4 Freelance Pillars
Translating corporate architecture into daily practice requires focusing on four actionable pillars that require minimal maintenance:
Cryptographic Credential Isolation
Never share or reuse passwords across clients. Generate unique 20+ character passwords for every portal and isolate vault entries using a dedicated password manager.
Continuous Multi-Factor Verification
Mandate 2FA on every service. Prefer hardware FIDO2 keys (YubiKey) or authenticator apps over insecure SMS codes, treating every session as untrusted until validated.
Hostile Network Perimeter Model
Operate under the assumption that all local Wi-Fi networks are monitored. Route sensitive traffic through an audited, zero-logs WireGuard VPN tunnel whenever working remotely.
Least-Privilege Scoping & Offboarding
Request only the exact permissions needed for deliverables. Immediately revoke API tokens, SSH keys, and cloud drive permissions the moment an engagement concludes.
Do not design your daily workflow hoping you will never encounter malware. Instead, adopt zero trust security by structuring your accounts so that even if one client credential leaks, the blast radius is strictly contained and cannot spread to other client files or your personal banking.
05 Real-World Scenario: The 3-Month Client Project Handoff
Zero trust concepts can feel theoretical until mapped onto concrete deliverables. Imagine a client hires you for a 90-day engagement, granting you administrator access to their WordPress CMS, Google Ads dashboard, and internal Slack workspace:
| Project Phase | Old Perimeter Instinct (High Risk) | Zero Trust Security Workflow (Protected) |
|---|---|---|
| Onboarding | Save client login credentials in default personal browser alongside personal accounts. | Spin up a dedicated, isolated browser profile (Chrome/Brave) tagged specifically for that client. |
| Access Level | Accept broad Super-Admin credentials without objection to avoid onboarding friction. | Request scoped Contributor/Editor role; elevate to Admin only during active migrations. |
| Daily Operations | Log in from open cafe Wi-Fi without VPN; leave sessions active indefinitely. | Enforce encrypted VPN tunneling; configure browser to purge session cookies on window close. |
| Project Handoff | Deliver final assets and leave dormant logins saved in your vault for future reference. | Formally request credential revocation, delete local staging databases, and wipe API keys. |
This disciplined compartmentalization guarantees that if the client suffers an internal compromise months down the road, your infrastructure cannot be implicated in the investigation.
06 Browser Compartmentalization & Endpoint Hardening
For web-based contractors, the web browser is your operating system. Without strict separation, a malicious script or tracking cookie on one tab can harvest session tokens from another tab.
Creating isolated browser profiles is the most effective zero-cost tactic in client compartmentalization. In Google Chrome, Brave, or Firefox, create separate profiles for each ongoing retainer:
- Profile A (Client One): Contains only Client One bookmarks, extension instances, and active logins.
- Profile B (Client Two): Completely quarantined cache, cookies, and local storage.
- Profile Personal: Reserved exclusively for personal banking, medical records, and social media.
You can test how identifiable your current browsing environment is by running our free Browser Fingerprint Test, and strengthen your endpoint defenses with our guide on Setting Up Two-Factor Authentication.
07 4-Phase Implementation Roadmap for Solo Operators
You do not need to overhaul your entire technical stack overnight. Successfully executing zero trust principles is about sequential, sustainable upgrades:
- Week 1 (Password Vault Quarantine): Audit your password manager. Eliminate every duplicate password and ensure all client portals use randomly generated 20+ character strings.
- Week 2 (Hardware-Backed 2FA): Transition from SMS verification to an app-based TOTP (Aegis, Ente Auth) or hardware security key (YubiKey 5C) across all primary email and hosting providers.
- Week 3 (Network Isolation): Configure an automatic kill-switch VPN on your primary laptop and mobile devices. Verify that local network file sharing is disabled on public connections.
- Week 4 (Access Offboarding Audit): Run a complete audit of dormant client permissions. Revoke stale OAuth connections in Google Workspace and GitHub.
For an exhaustive checklist covering every layer of your hardware and software, consult our comprehensive 15-Step Freelancer Cybersecurity Checklist and our blueprint for Building a Complete Security Stack for Freelancers.
08 Frequently Asked Questions About Zero Trust Security
Does zero trust actually slow down daily freelance work?
Can a solo freelancer realistically implement zero trust security without an IT department?
What is the single most important habit in zero trust architecture?
How does zero trust architecture protect against phishing attacks?
09 Final Verdict: Turning Security into a Client Selling Point
Practitioner skepticism regarding administrative friction is valid when organizations deploy clunky enterprise software. However, for an agile freelancer, embracing zero trust security provides an impenetrable operational shield without hindering productivity.
More importantly, advertising your adherence to zero-trust data hygiene sets you apart from amateur competitors. Discerning enterprise clients gladly pay premium rates to remote contractors who guarantee their credentials and proprietary source code will never be commingled or exposed.
SafeStackPro Architecture Verdict
Treat every network as compromised, every device as unverified, and every client environment as strictly isolated. By systematically eliminating implicit trust, you insulate your freelancing business against modern cyber threats.
